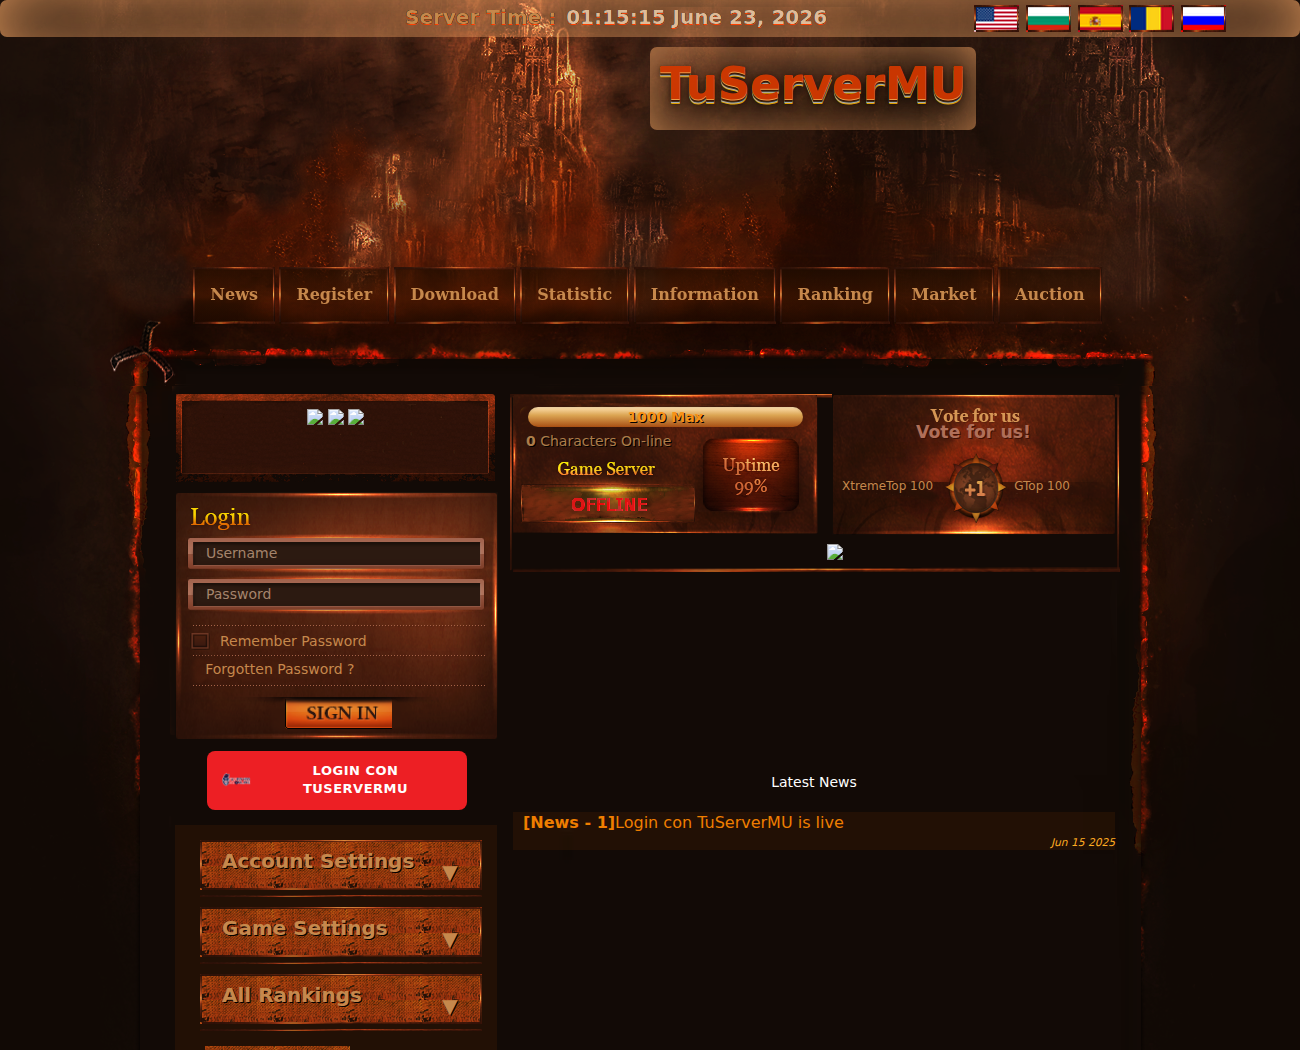
A plugin for the DT-Web 2.0 (r00tme) MU Online CMS. It adds a “Login con TuServerMU” button, then links the player's existing in-game MEMB_INFO account by verified email or provisions a new one, and signs them in. Rides DT-Web's own mssql_*→sqlsrv shim, so it runs on PHP 8.x. Tested end-to-end and working.
Copy the four files into the matching folders of your DT-Web install, then register two routes and add the button.
At Account → OAuth apps, create a Confidential app with redirect URI:
https://your-site.com/?p=ssocallback
Drop them into your DT-Web folders:
inc/tsm_sso_lib.php
configs/tsm_sso.php   (edit your Client ID / Secret)
mod/ssologin.php
mod/ssocallback.php
In inc/loader.php, next to the other $active_pages[...] entries, add:
$active_pages['ssologin']    = 'ssologin.php';
$active_pages['ssocallback'] = 'ssocallback.php';
Paste the snippet from BUTTON-SNIPPET.html into your active theme's login template (default Aion: themes/Aion/menus/login_form.php; other themes: themes/<theme>/menus/user_panel.php):
<a class="tsm-sso-btn" href="?p=ssologin">
  <img src="https://sso.tuservermu.com/sso/img/sso-logo.png" height="18">
  Login con TuServerMU
</a>
/?p=ssologin - sends the player to TuServerMU (Authorization Code + PKCE)./?p=ssocallback - exchanges the code, reads the verified profile, links the MEMB_INFO row by email or provisions a new account (respects your $option['md5'] password scheme + DT-Web's companion rows), then seeds $_SESSION['dt_username'] / ['dt_password'] exactly like a normal login.Run DT-Web on PHP 8.1–8.4 (8.5 not verified). ODBC18 users: if the SQL connection fails on TLS, add "TrustServerCertificate" => true to the shim's $connectionInfo in configs/config.php (a DT-Web/driver matter, not the plugin).
Questions? [email protected] · Full OIDC docs